 EN
 RO
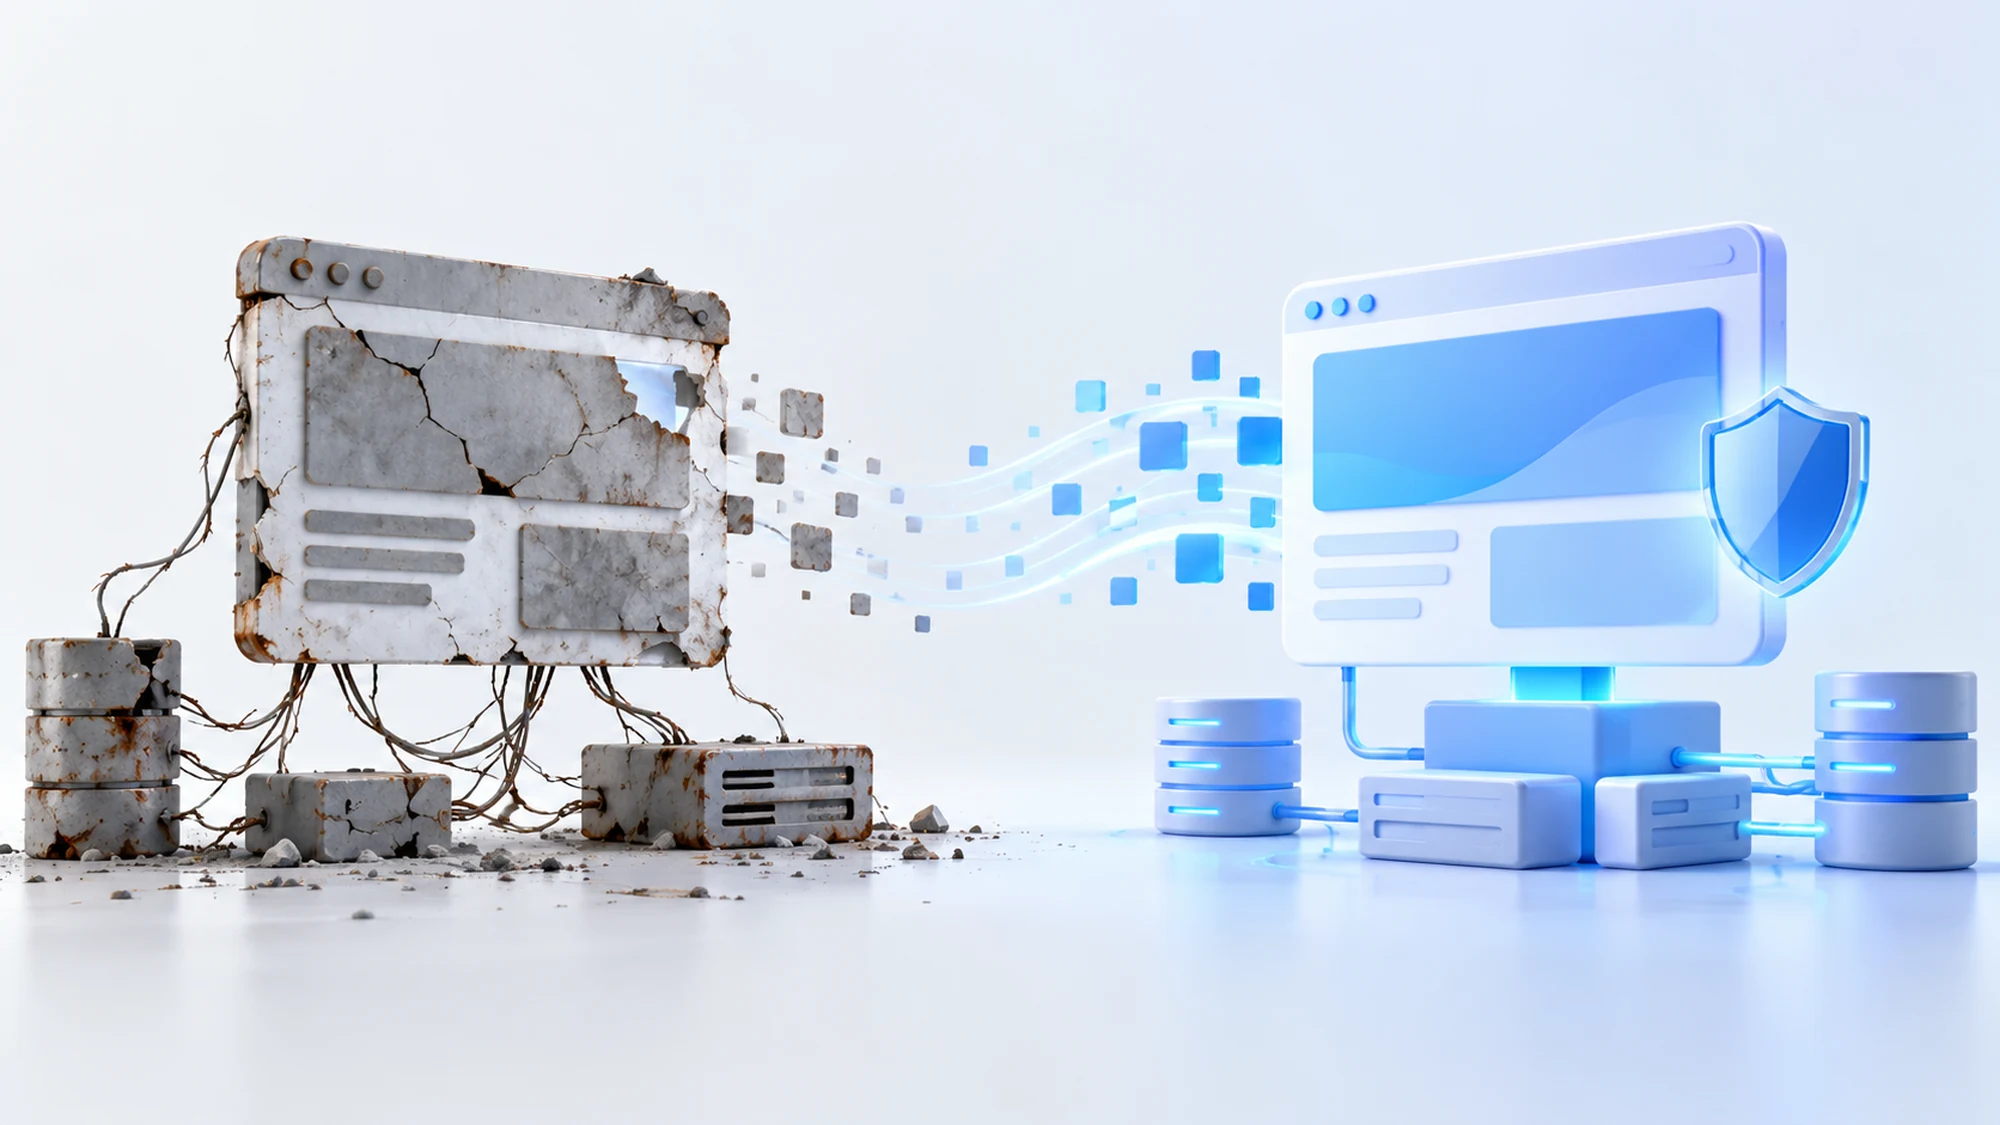
A website that looks normal can, at the same time, be an open door for attackers. An old website becomes a security risk when its code, platform or dependencies stop receiving updates, even if the page loads without any visible errors. The difference between "it looks fine" and "it's secure" isn't visible from the front end — it's in the code running behind it.
The problem builds up gradually: a plugin left unpatched for two years, a CMS that reached a version without support, a contact form without real validation. None of these signals stop the site from working, but each one widens the attack surface. This article walks through the concrete signals you can check yourself, then explains what modernizing this kind of site on Laravel actually looks like in practice.
Why an "old" website isn't just about outdated design
When people hear "old website," most think of dated design or a layout that doesn't work well on mobile. The real risk lies elsewhere: in the code processing forms, in the PHP version running on the server, in plugins nobody maintains anymore.
A website can have a fresh design, redone a year ago, and still run on a technical core that's six years old, with dozens of already-documented public vulnerabilities. Design and technical security are separate layers — a site can be good-looking and vulnerable at the same time.
The technical signals that show your online presence has become vulnerable
The following signals don't require advanced security knowledge to spot. Most can be checked directly by a site administrator or a developer within an hour.
- CMS or framework that reached a version without official support — for example a WordPress, Joomla or custom framework version that no longer receives security patches from its maintainer.
- Plugins or modules left unupdated for over a year — every abandoned plugin is a potential vulnerability, publicly documented and searchable by anyone.
- PHP or another runtime running an End-of-Life version — runtimes without support no longer receive fixes, not even for already-known critical issues.
- Expired SSL certificate or connection without HTTPS — modern browsers explicitly flag these sites as unsafe to visitors.
- Forms without validation or anti-spam protection — a sign that user input isn't properly filtered before reaching the database or an inbox.
- Passwords and admin access unchanged for years — especially if access was shared with former agencies or freelancers no longer working with the business.
- No automated backups at all — without a recent backup, a successful attack or a human error can mean total data loss.
Signals visible at the business level, not just in the code
Not every signal requires code access to spot. Some show up directly in day-to-day business activity and are often the first indicators visible to a manager or business owner.
- Google Search Console shows "dangerous content" or "site compromised" warnings.
- Customers report strange emails or pages that appear to come from the business domain, but weren't sent by the in-house team.
- Organic traffic drops suddenly, with no obvious marketing cause — a frequent symptom of a spam-content infection invisible to the average visitor.
- The site suddenly becomes very slow or starts sending large volumes of email, without the team having launched any campaign.
Each of these signals, taken alone, can have other explanations. Combined with one or more of the technical signals from the previous section, though, they point almost certainly to a security problem that's already active, not just potential.
What actually happens when these signals are ignored
Delaying a fix doesn't usually mean "nothing happens" — it usually means the problem becomes visible later, and more expensive to fix.
- Risk: a vulnerable plugin stays unpatched for months. Mitigation: periodic dependency audits and disabling unused plugins, not just updates on request.
- Risk: public forms don't correctly validate submitted data. Mitigation: validation on both the client and server side, before any processing or storage.
- Risk: admin access is shared with people no longer working with the business. Mitigation: periodic review of accounts with access and immediate deactivation of unused ones.
- Risk: no recent backup exists at the moment of an incident. Mitigation: automated backups, tested periodically through real restores, not just generated and forgotten.
A compromised website usually means more than development time for cleanup: it means temporary deindexing from Google, browser warnings for visitors, and in some cases mandatory notification to customers whose data may have been exposed.
Quick fix vs full modernization: how to decide
Not every signal above requires rebuilding the entire website. The difference between a targeted fix and a full modernization mainly depends on how many technical layers are affected at the same time.
A targeted fix is enough when the problem is isolated: an expired SSL certificate, a plugin update, a password to change. These get resolved in hours, without affecting the rest of the application.
Full modernization becomes necessary when multiple signals coexist: unsupported CMS, End-of-Life PHP, several abandoned plugins, code written ad-hoc over the years by different developers. At that point, repeated patching costs more in the long run than rebuilding on a solid technical foundation — because every further update risks breaking something else in the same fragile codebase.
A practical rule of thumb: if you've needed more than two emergency security-related interventions on the same site in the last 12 months, the conversation about full modernization deserves to be taken seriously, not postponed again.
What modernizing an old website on Laravel actually looks like
At HappyWeb, modernizing an old website doesn't just mean "we rewrite it in another technology" — it means a controlled migration, with verifiable steps at every stage.
- Initial technical audit — a full inventory of versions, plugins, integrations and existing data, so you know exactly what's being migrated.
- Prioritizing critical data and features — what must be kept identical (content, SEO, URLs) and what can be rebuilt differently.
- Building the application on Laravel — with authentication, data validation and role management treated as baseline requirements, not later add-ons.
- Data migration and parallel testing — the new application runs tested before the domain is finally switched over.
- 301 redirects for old URLs — to preserve rankings already earned in Google and avoid broken links.
- Ongoing maintenance plan from launch — so the new application doesn't end up, years from now, in the same spot as the site it replaced.
The advantage of an application built on Laravel, compared to a platform with dozens of independent plugins, is that maintenance concentrates in a single codebase controlled by one team — a point covered in more detail in the comparison between custom and WordPress maintenance.
Summary table: signal, real risk, recommended action
| Observed signal | Real risk | Recommended action |
|---|---|---|
| Unsupported CMS/framework | Known vulnerabilities, no patch available | Full modernization |
| End-of-Life PHP version | No security fixes at runtime level | Full modernization |
| Abandoned, unupdated plugin | Publicly documented entry point | Immediate removal or replacement |
| Expired SSL certificate | Browser warning, loss of trust | Urgent targeted fix |
| No tested automated backup | Total data loss on incident | Urgent targeted fix |
| Uncontrolled shared admin access | Compromise via old/forgotten account | Urgent targeted fix |
Frequently asked questions
How do I know if my website is already compromised, not just vulnerable?
Check Google Search Console for security warnings, look for unfamiliar pages or files in the site structure, and compare recent organic traffic with earlier periods. A sudden drop with no marketing explanation is a signal worth checking immediately.
Can an old website be modernized without losing its Google ranking?
Yes, if the migration preserves the relevant content structure and uses correct 301 redirects for old URLs. Ranking loss usually happens when migration is done unplanned, without mapping old URLs to the new ones.
Why Laravel and not another platform for modernization?
Laravel includes security mechanisms out of the box (CSRF protection, data validation, role management), without depending on third-party plugins with their own update cycles. That reduces the number of independent components that can each become a weak point.
How long does a full modernization of an old website usually take?
It depends on the complexity of the existing site and the volume of data to migrate; a simple presentation site modernizes faster than an application with multiple integrations. The exact timeline is set after the initial technical audit, not before it.
Is it worth waiting for the next incident before modernizing?
That's not a recommended approach. The cost of a planned modernization is usually more predictable than the cost of recovering from a real incident, which also includes downtime and potential loss of customer trust.
Conclusion
An old website doesn't turn into a security risk overnight — it happens gradually, through unpatched plugins, unsupported versions and uncontrolled access, piling up year after year. Recognizing these signals early lets you choose between a quick fix and a full modernization, before that decision gets made for you by a real incident.
Want a clear audit of your current website before deciding between patching and modernizing? Contact us for a discussion about your project. See also our web development services.
Write a comment